AI adoption is accelerating, but enterprise security controls aren't always keeping pace. As organizations introduce AI agents, internal MCP servers, and new AI-powered workflows, they face growing challenges around identity, access, sensitive data, and API governance.
The challenge isn't necessarily building an entirely new AI security stack. It's ensuring that existing security controls can support an increasingly AI-driven operating environment.
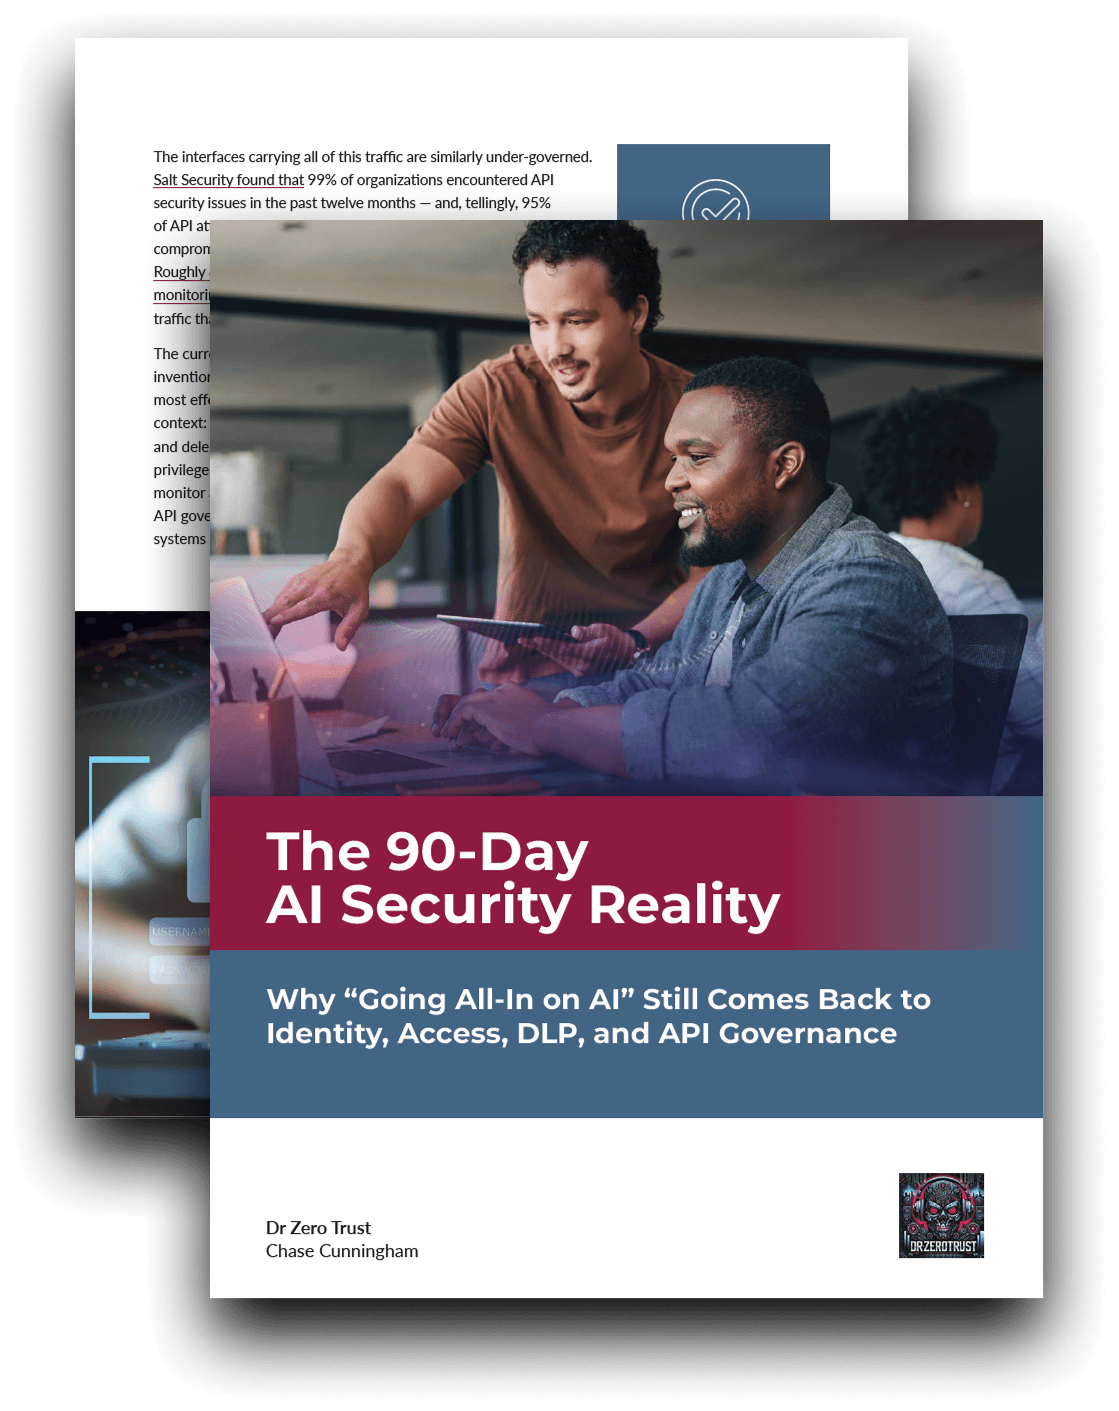
In The 90-Day AI Security Reality, Dr. Chase Cunningham examines why security leaders facing aggressive 90-day AI mandates should strengthen foundational security practices to support AI adoption without introducing unnecessary risk.
Of technology leaders say AI adoption is outpacing their organization's ability to manage associated risks. (EY, 2026)
Of organizations worldwide have achieved mature AI security readiness. (Cisco, 2025)
Of organizations that experienced an AI-related incident lacked proper AI access controls. (IBM, 2025)
These findings highlight a growing disconnect between the pace of AI deployment and organizations' ability to secure it.
01
End-to-end visibility from mainframe to microservices to mobile with all telemetry (metrics, logs, traces, events) in context.
02
Advanced root cause analysis, anomaly detection, and remediation guidance at scale.
03
Detects issues others miss by combining broad default alert coverage with causal AI to uncover problems before users notice.
04
High-speed, schema-on-read querying of logs, events, business, and security data.
05
Real-time vulnerability detection, exploit prevention, and Kubernetes Security Posture Management (KSPM).
06
Build tailored automation and platform extensions for unique business requirements.
07
Built-in support for OpenTelemetry, OpenSLO, and 750+ supported technologies.
08
OneAgent® detects, instruments, and baselines every component automatically.
09
Learns “normal” behavior, adapts dynamically, and updates agents automatically to minimize maintenance.
10
Advanced digital experience monitoring across web, mobile, and API layers.
11
Real-time observability for microservices, serverless workloads, and container platforms.
As organizations deploy AI agents, MCP servers, and AI-powered workflows, they introduce new identities, access requirements, and data flows that existing security programs may not be fully equipped to govern.
Many AI security challenges stem from familiar gaps in identity management, access controls, data loss prevention (DLP), and API governance. The report examines why these foundational security disciplines remain critical in emerging AI environments.
Organizations can accelerate AI deployment by building established security controls into development workflows from the start. The report explores why consistent identity, access, DLP, and API governance practices can help teams move toward production while keeping policy enforcement and auditability in place.
Discover the research and expert perspectives behind today's AI security challenges, including why established security fundamentals remain essential as organizations move from AI experimentation to enterprise-scale adoption.
As organizations expand their use of AI, understanding how existing security controls apply to emerging technologies is increasingly important. Connect with Arctiq to discuss your AI security priorities and challenges.